
AWS S3 and IAM Access
Provision S3 buckets yourself from the Catalog, and learn when and how to request IAM users or bucket policies from CTO2B.
Your applications run inside CTO2B-managed AWS accounts. Two kinds of AWS
access come up regularly — object storage (S3 buckets for uploads, exports,
backups) and IAM access for a service or a team member. The boundary is
simple: buckets are self-service from the Catalog, while IAM changes go through
a request.
On GCP? See GCP IAM and GCS Access.
S3 buckets — provision them yourself
S3 buckets are Components, provisioned the same way as databases or caches.
-
Go to Applications → Deployments and click + New.
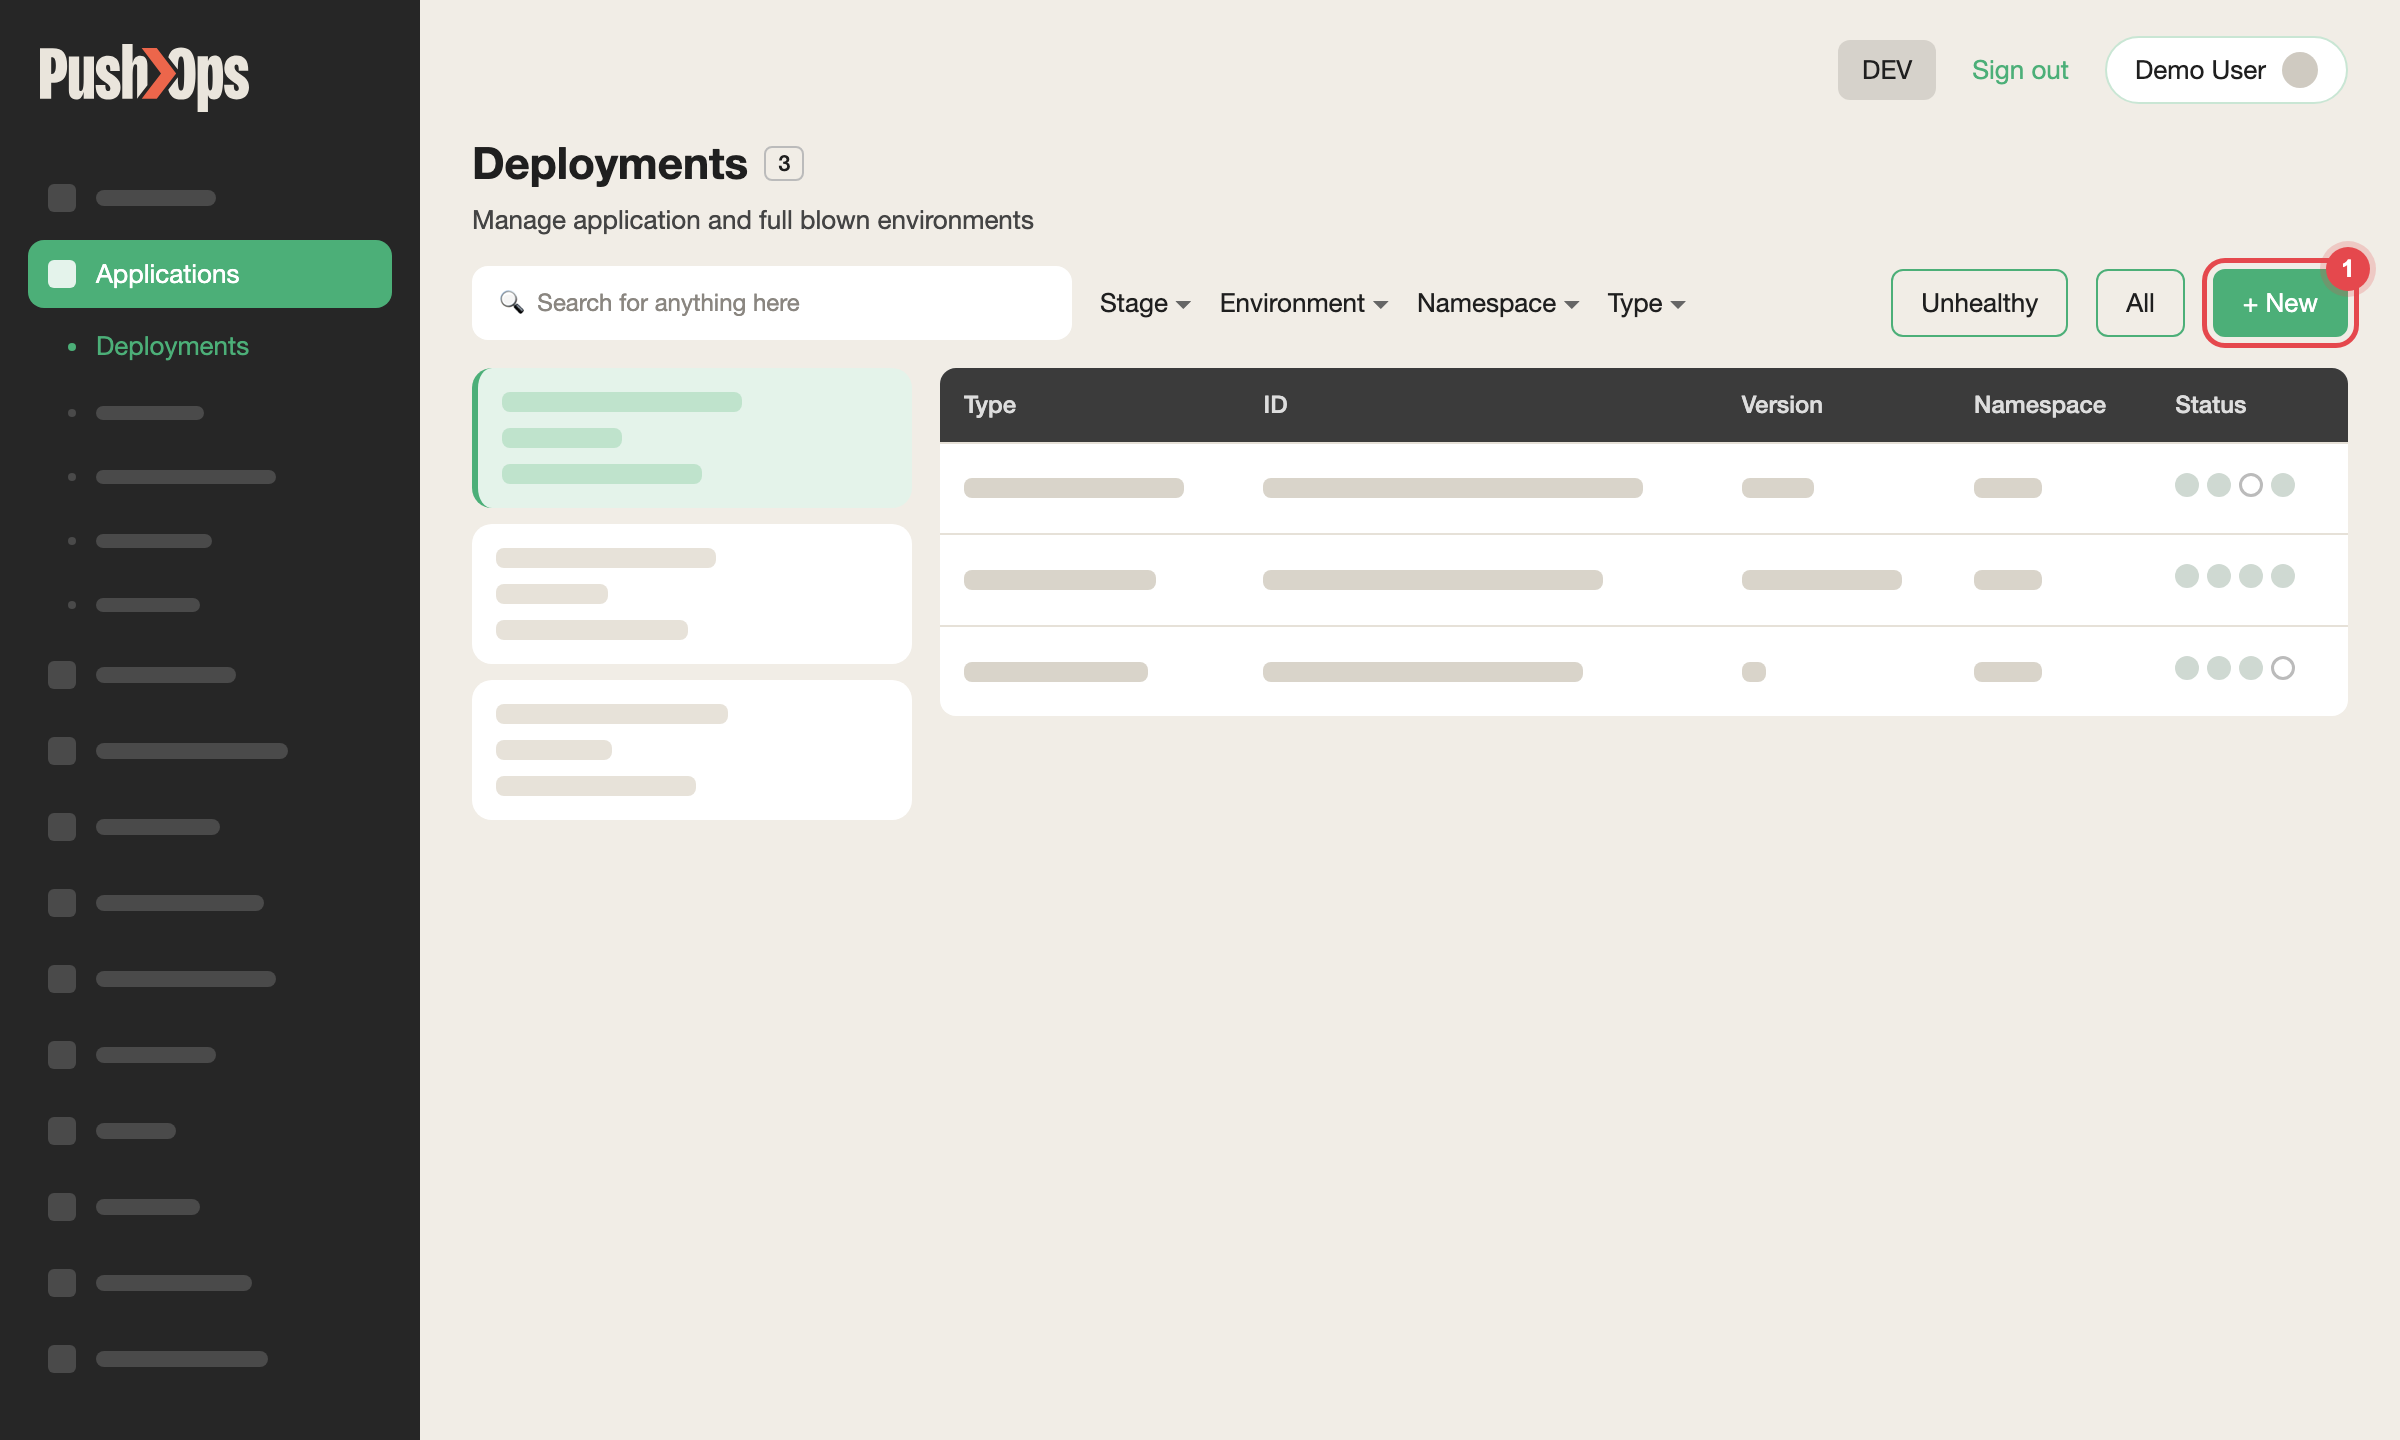
Figure 1 — Applications → Deployments: click + New
-
Under ENVIRONMENTS, select the Environment.
-
Under APPLICATIONS, which appears once an Environment is selected, select the S3 bucket Catalog item (under AWS Services).
-
Choose the SERVICE and NAMESPACE, and enter a NAME.
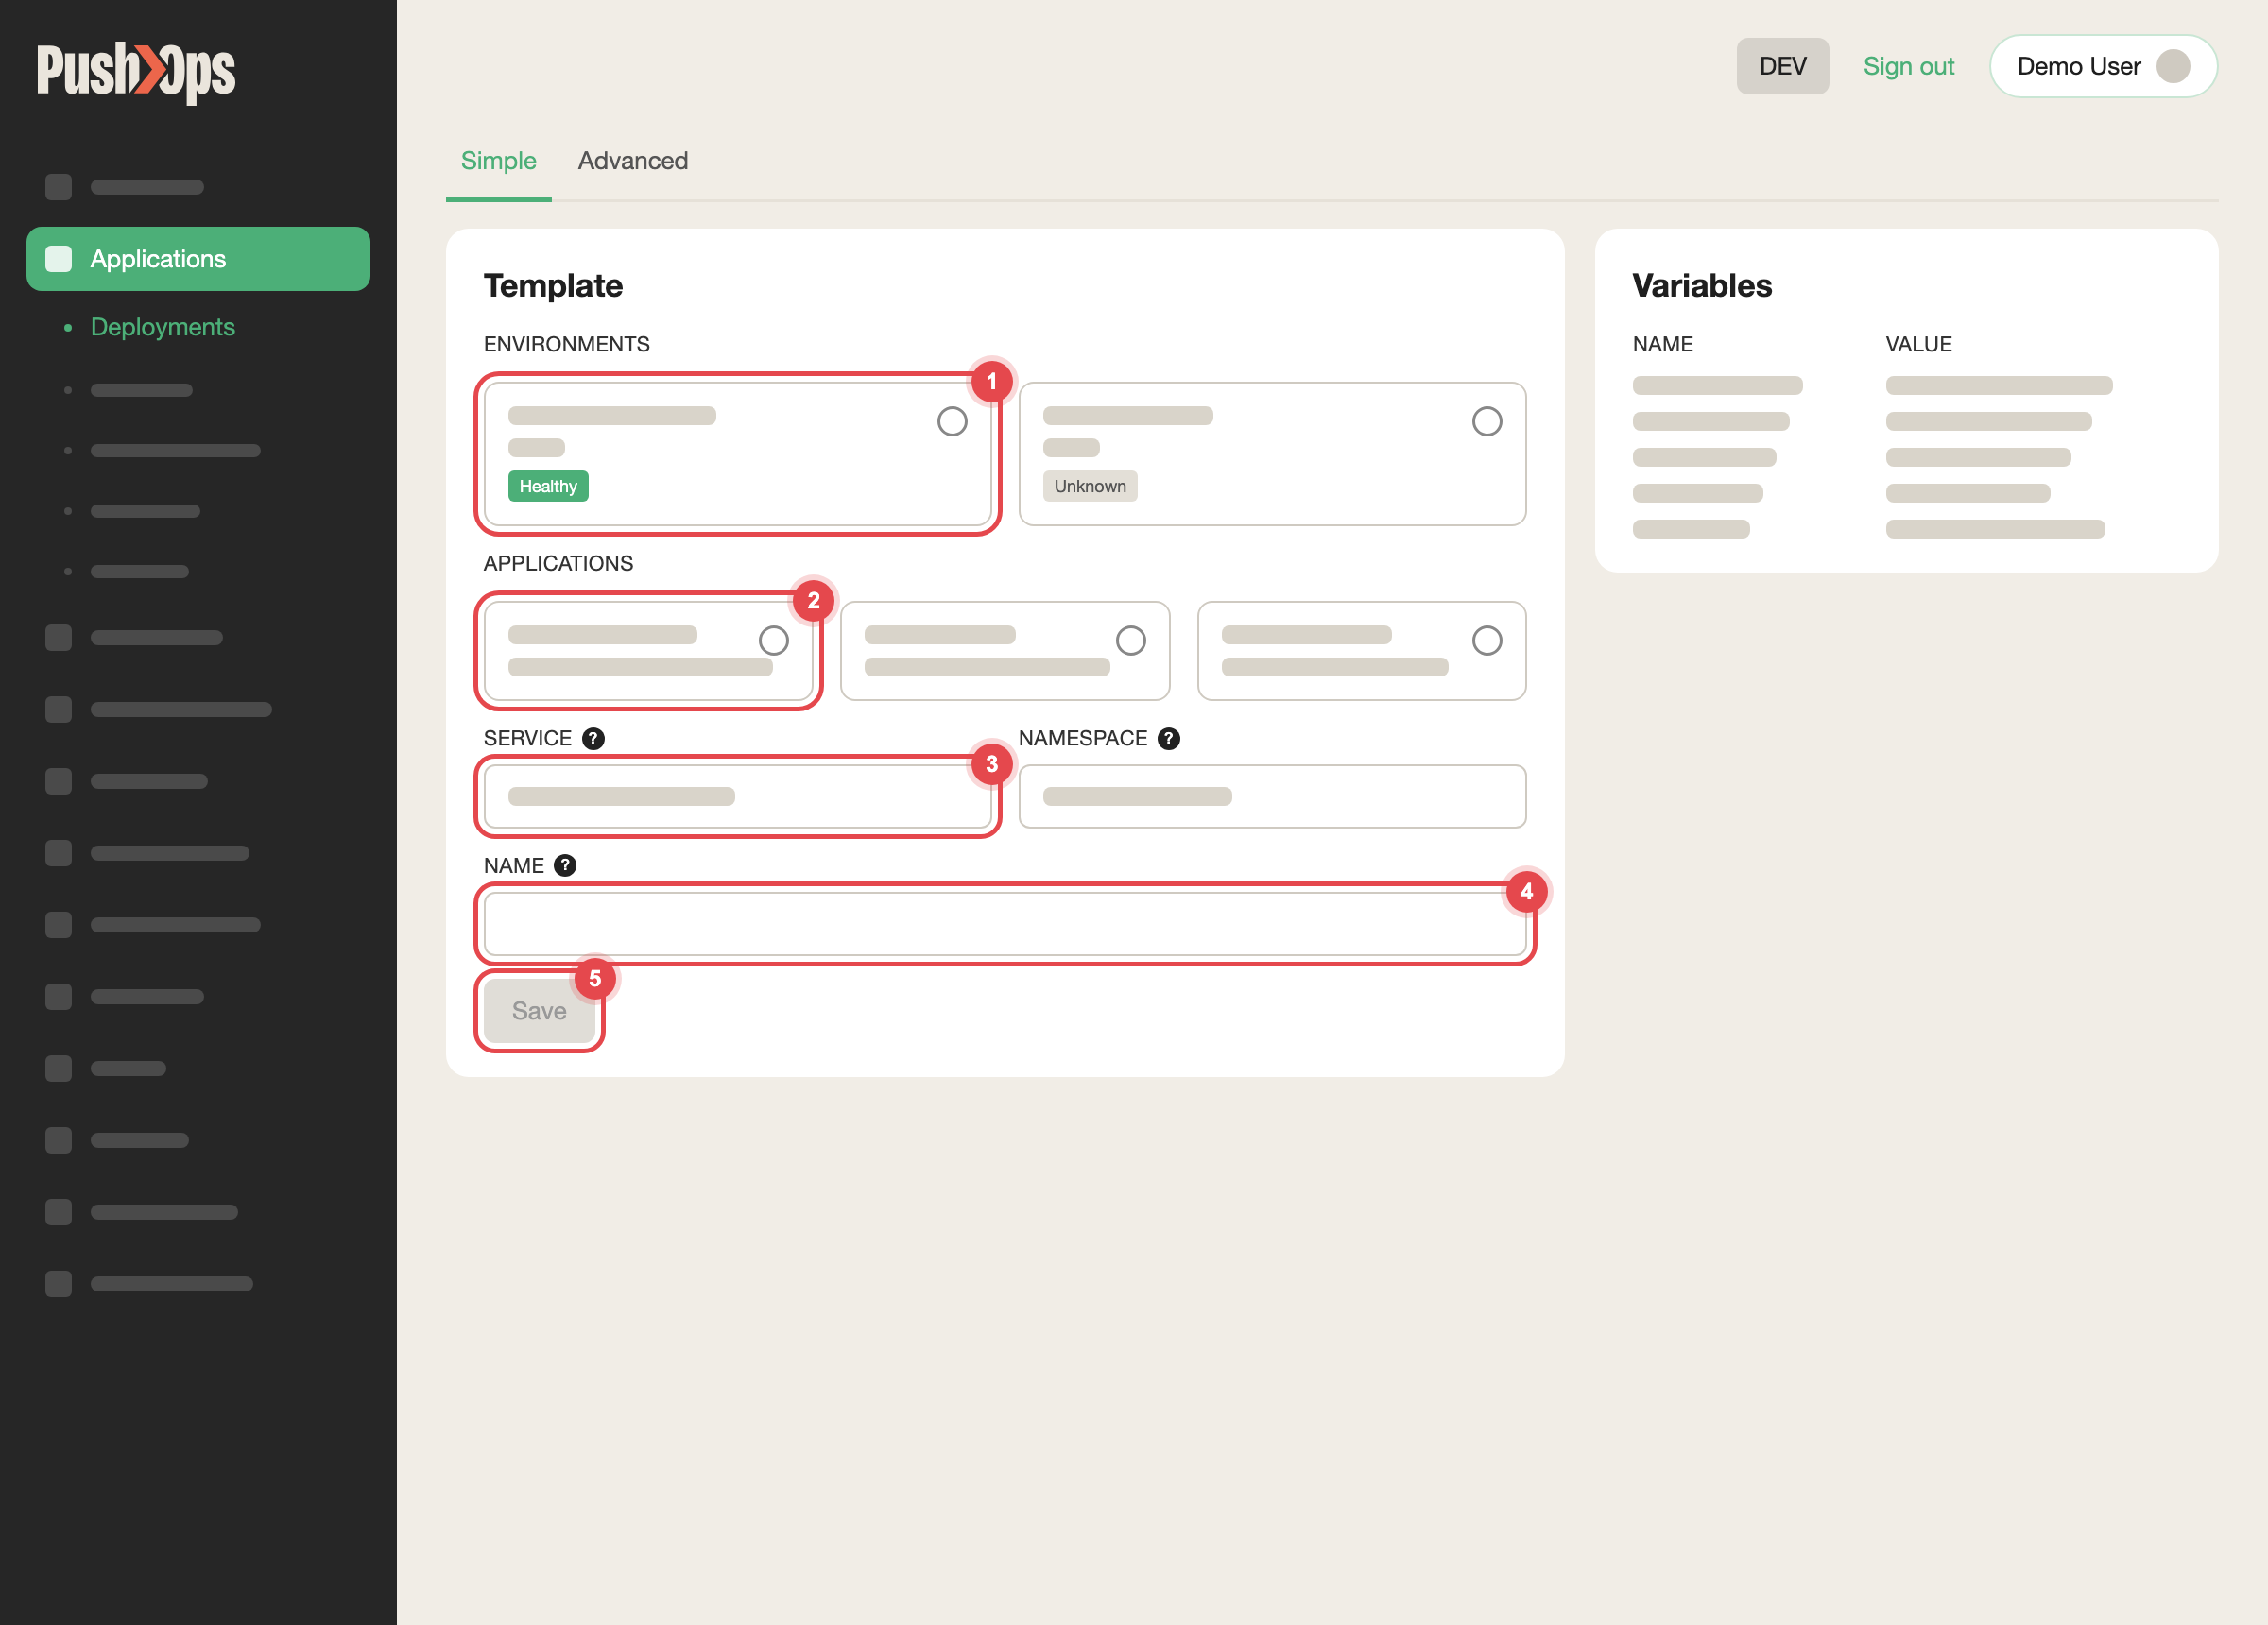
Figure 2 — Choose the environment, the Catalog item, the Service and a name, then click Save
-
Fill in the configuration — region and access tier.
-
Click Save. The platform provisions the bucket and injects the access
credentials into your Service automatically.
Connection details and credentials appear on the Component's dashboard once
provisioning completes. Your application reads the bucket using the injected
credentials, so no manual IAM configuration is needed.
AWS IAM access — raise a request
The following are not self-service:
- IAM users for third-party integrations, such as a CI/CD pipeline or an
external SaaS tool - Bucket policies for cross-account or cross-service access
For a person who needs the AWS Console, use temporary role access instead of
an IAM user — see
Temporary AWS Console Access Through Teleport.
How to request: raise a request through the Support Portal. If you have a
shared Slack channel with CTO2B, you can raise it there as well — it reaches
the same team, but the Support Portal gives the request a ticket you can track.
Include:
- What you need access to — for example, "read access to the
my-exportsS3
bucket from our CI pipeline" - Which environment it affects (dev, staging, or production)
- Whether it is temporary or permanent
CTO2B creates the IAM policy and shares the credentials or ARN with you.
Scope the request narrowly: list only the actions and resources the integration
actually needs, rather than a broad grant.
About your AWS account
Your environments run in CTO2B-managed AWS accounts, and each customer's
environments are isolated — your production workloads do not share an account
with another customer. Per-environment cloud costs are visible in SVIEW.
For questions about your specific account structure, ARNs, or Organisation-level
configuration, raise a request.
Common questions
Can I create IAM users myself?
No. IAM user creation is not self-service — raise a request with the details
above.
My bucket type is not in the Catalog. Can I still request one?
Yes. Raise a request with your requirements and the team will provision it and
return the credentials.
I need to give another AWS service access to my bucket.
That is a cross-service IAM policy request. Raise a request with the source
service's ARN and the permissions needed (read, write, or delete).
I need a pre-signed URL for temporary file access.
Pre-signed URLs are generated by your own application using the credentials
injected into the Component. No platform-level action is needed.
My application needs AWS access without any credentials in its config.
Use an IAM Service Account instead of an IAM user — see
IAM Service Accounts.
Related articles
Updated about 1 month ago